TL;DR
If you mean an input PIN for account verification, start with one labeled text input that keeps the code as a string. Make paste and manual entry work, consider autofill for one-time codes, and let the server decide whether the code is valid. Use visual slots only when they preserve that single-field experience. An electronic input pin is a different subject entirely.
A search for input pin can lead to hardware discussions about signals on a device, or to a screen asking someone to enter a PIN. This guide is about the second meaning, specifically a verification-code field in a Vue application. The distinction matters: a hardware input pin is configured on a circuit or controller, while an authentication field collects a human-entered secret for a verification flow.
There is a second ambiguity within the interface itself. A one-time code arrives through a message or authenticator and has a limited lifetime; a persistent PIN is chosen or reused by the account holder. They may both have six characters on screen, but they should not inherit the same autocomplete, expiry, or resend behavior. I would settle that product contract before selecting a component.
If you need the detailed Vue implementation, our existing accessible pin-input walkthrough covers native markup and entry tests. Here I focus instead on the decisions and states a team should agree on before building or integrating the field.
Table of contents
- First, define what the PIN represents
- Choose one logical field, even if the design shows six cells
- Specify entry behavior before styling the component
- Treat validation and recovery as a state contract
- Where Vue state belongs
- Review the experience as a flow, not a screenshot
- Frequently asked questions
- Build the contract before the visual slots
- Sources
- Recommended Reads
First, define what the PIN represents
Write down who issues the value, its allowed characters and length, what ends its validity, and which server challenge it belongs to. For example, an illustrative six-digit one-time code might be 004812; keep it as a string so both leading zeroes survive. Do not silently assume every provider uses six digits, or that a new code invalidates the previous one. Those are server contract decisions.
| If the person enters… | The interface needs to explain… | Do not assume… |
|---|---|---|
| A one-time code from a message | Where it was sent, how to enter or paste it, and how to request another | A persistent secret or a guaranteed SMS autofill suggestion |
| A code from an authenticator app | Which app to consult and what to do if access is lost | That a resend button can issue a replacement app code |
| A persistent account PIN | Where it is used and how to recover or change it | That it expires after a short countdown |
The distinctions affect copy as much as code. “Enter the code from your authenticator app” is more useful than “Input PIN”; “Send another code” makes sense only when the system can actually send one. For existing-user sign-in, W3C’s accessible authentication guidance specifically addresses the burden of transcribing a one-time passcode and the importance of mechanisms such as paste or autofill.
Choose one logical field, even if the design shows six cells
A native text input is my default for a verification code. It supports familiar text editing, selection, paste, and keyboard navigation without making a person discover six separate focus stops. For an issuer-defined numeric code, use a text value rather than a number field: Google’s SMS OTP form guidance recommends type="text", inputmode="numeric", and autocomplete="one-time-code" for SMS one-time codes. The latter two are hints for supported keyboards and autofill, not proof that a code is valid. Match the input mode and autocomplete behavior to the actual code type.
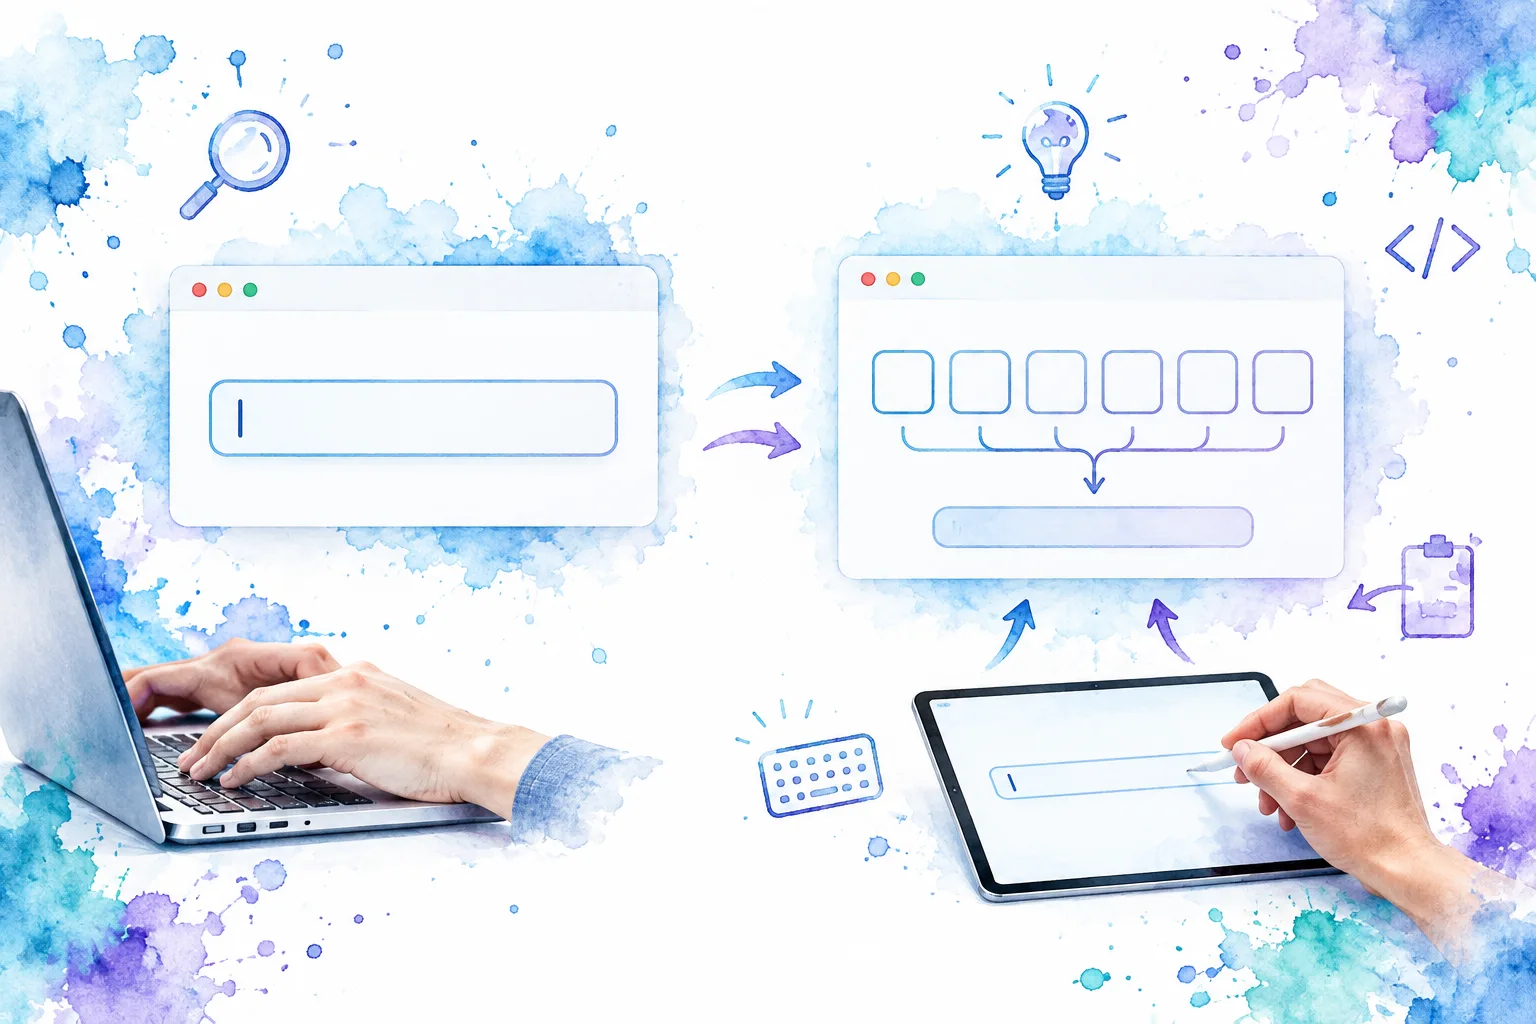
Six visible slots can still be useful when a product wants to show character count and progress. Prefer one real editable input behind that presentation, with decorative slots reflecting its value, rather than six independent values that must be stitched together. If your design truly requires six editable controls, define how full-code paste, Backspace, arrows, mobile autofill, focus, and assistive-technology announcements work before adopting it. W3C illustrates a failure in which pasting a complete code into six separate inputs fills only the first cell. A polished layout does not repair that interaction. See the W3C example.
The following verified video is a visual introduction to constructing a PIN input with HTML, CSS, and JavaScript. Treat it as a UI companion, not as a substitute for a verification service or an accessibility review.
Specify entry behavior before styling the component
A good entry contract describes what happens to the whole value when someone types, pastes, edits, or autofills. For a six-character example, 004812 must remain 004812 from the field through the API request. Test a full paste while the cursor is in the middle of an existing value, not just into an empty field. Decide whether spaces copied from a message are accepted and normalized; never rewrite an unfamiliar format into a different code without making that policy explicit.
Keep a visible label, such as “Verification code,” separate from a short instruction that names its source. Associate an error message with the control rather than relying on color, and give the real focus target a visible focus indicator. If the code is incomplete, let a person finish it instead of announcing an error at every keystroke. The W3C authentication guidance makes pasting and autofill especially consequential in authentication, not optional cosmetic conveniences.
Autofill should populate the same value path as typing. SMS suggestions vary by platform, message format, and support, so a manual entry and paste fallback must remain available. Google’s SMS OTP form guidance explains the origin-bound message format and treats a basic native input as the interoperable starting point. If you offer a Verify button, do not send a request merely because the sixth slot filled: the person may still need to correct an autofilled or pasted value.
Treat validation and recovery as a state contract
A code-shaped string is not an accepted authentication challenge. The client can identify missing characters or an unsupported format; only the service that issued the challenge can decide whether the value is current, belongs to the right attempt, or has already been consumed. I would specify the following UI outcomes with the API team before wiring up a form:
| State | What the person should see or be able to do | Ownership |
|---|---|---|
| Incomplete | Calm format guidance and an editable value, without premature failure alerts | Field |
| Submitting | A clear progress state and protection against duplicate requests | Vue request state |
| Incorrect | Actionable retry feedback without deleting entered work unnecessarily | Server result and field display |
| Expired | An explicit expiry message and an available recovery path | Server result and flow |
| Rate-limited | The next permitted action or wait instruction, not an endless retry loop | Server policy |
| Resent | Confirmation of what happened and a clear path back to entry | Server result and flow |
| Verified | Advance only after the server accepts the challenge | Server result |
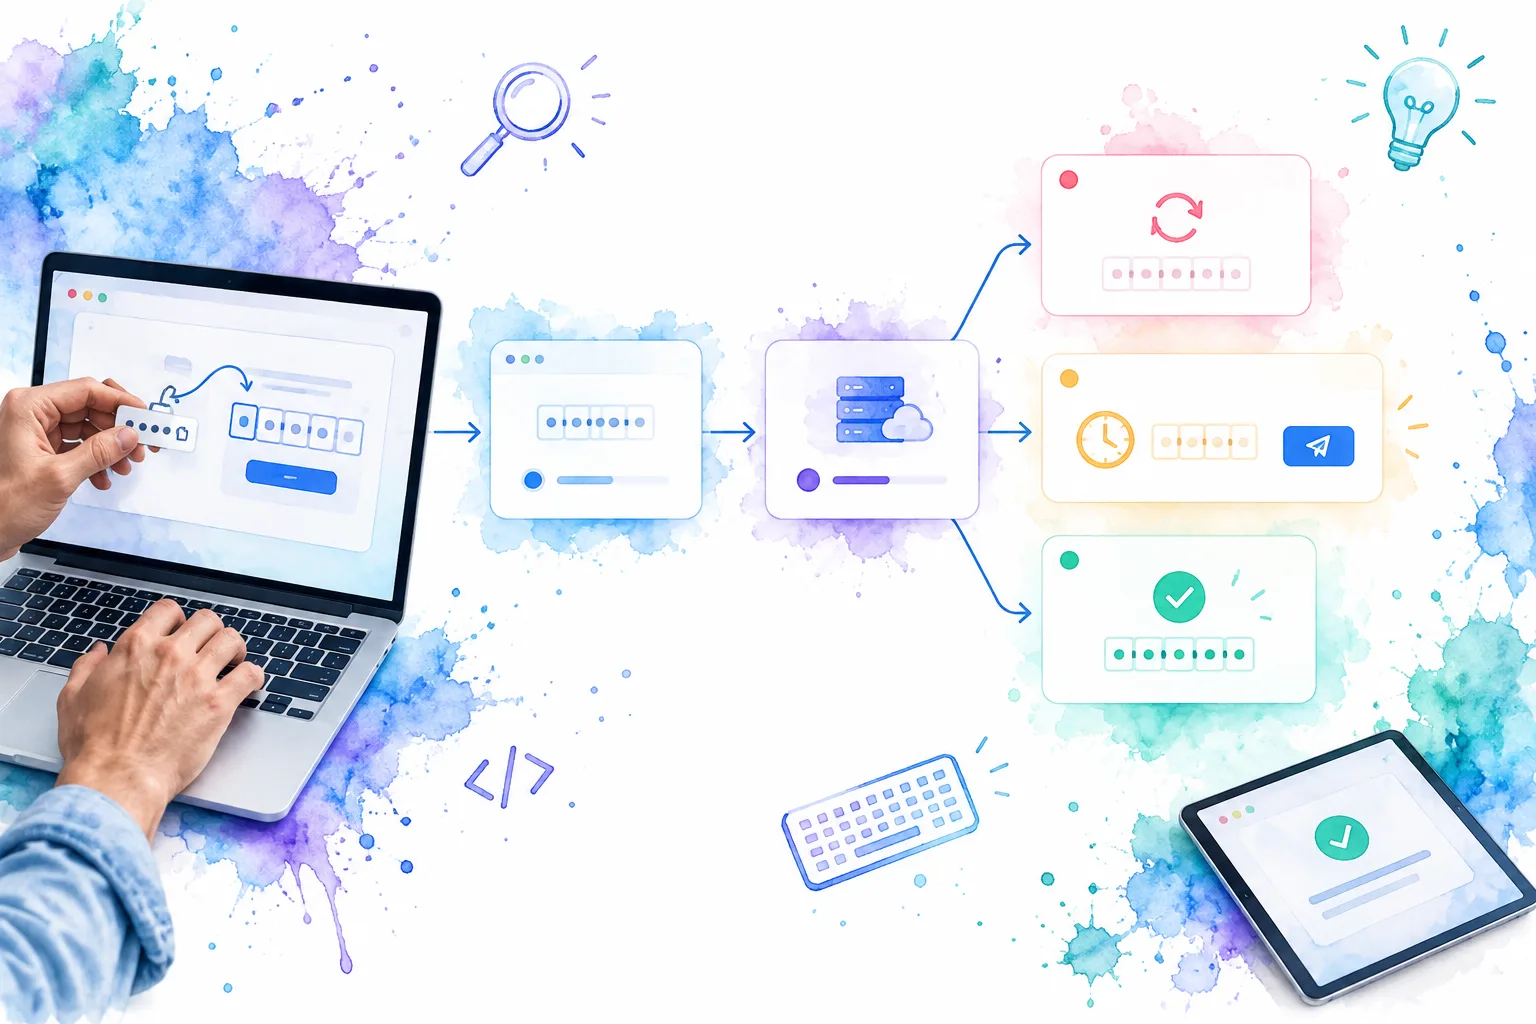
There is a subtle race: a verification response for an old challenge might arrive after the user requests a new code. Tie results to the challenge that produced them, and ignore obsolete responses in the UI. A resend action also needs a documented rule for whether it replaces earlier codes. OWASP’s MFA guidance recommends short-lived, single-use OTPs, attempt limits, and issuing a fresh value on resend rather than treating the input widget as the security boundary.
Do not announce each digit as a status update. Announce consequential changes such as “New code sent” or a failed submission once, then keep keyboard focus predictable. If the server returns an expired state, say “This code expired; request a new one” rather than mislabeling it as a typing mistake.
Where Vue state belongs
In Vue, keep one string value for the editable code. A local format check can derive an incomplete state from that string, while separate reactive state tracks a pending request and the server’s latest outcome. A reusable control can accept a modelValue and emit update:modelValue so the parent form owns the value; Vue’s component v-model documentation describes that prop-and-event contract. Do not make each visual cell an unrelated form field.
The parent flow, not a decorative slot, should own the challenge identifier, resend result, expiry status, and submission handler. When an input edit makes a previous “incorrect code” message stale, clear or update that message deliberately. When the challenge changes, decide whether the old field value should be cleared; do not accidentally keep an old code visible as if it belonged to the new request. When a request finishes, check that it still corresponds to the currently displayed challenge before changing the screen.
If you are integrating with DOM Studio, its Form reference describes named child values and runtime field errors. A purpose-built verification control can join that form contract with one named string value. DOM Studio’s Code Input, despite the similar name, is documented as a structured-text editor, not an OTP component. Our step-up verification block illustrates a broader sensitive-action dialog with method choice; its example shows UI readiness, and its integration notes explicitly call for a server-issued challenge. Use it as a flow reference, not as evidence that a visual demo alone verifies an account.
Review the experience as a flow, not a screenshot
Before release, try a code starting with zero, a full paste, a corrected middle character, and manual entry without autofill. Repeat with keyboard-only navigation and the browser and screen-reader combinations your product supports. Confirm that the label and error describe the same real field when slots are displayed. Ask someone unfamiliar with the screen to identify where the code comes from and what happens after an expired attempt.
Then exercise two network sequences: first, submit twice while verification is pending; second, request a new code while an earlier response is still outstanding. Neither should create an unintended success state. Test incorrect, expired, reused, and rate-limited outcomes with your backend, not only mocked red borders. OWASP’s OTP handling recommendations place expiry, single-use enforcement, retry controls, and avoiding OTP values in logs outside the input component.
Frequently asked questions
Is an input PIN the same thing as an electronic input pin?
No. In this guide, it means a field where a person enters a verification code or PIN. Hardware input pins are electrical interfaces, not authentication form controls. If your task involves reading a signal on a board, a Vue verification field will not solve it.
Does a completed code mean verification succeeded?
No. Completion says only that the input matches the expected shape. The issuing service must check the relevant challenge and return the authoritative result before the app treats the user as verified. OWASP’s OTP guidance covers expiry, single use, and attempt limits.
Build the contract before the visual slots
I would first agree on the code’s source, format, challenge lifecycle, feedback, and recovery path. Then I would start with a native single input and add segmented presentation only if its paste, focus, and accessibility behavior survives real testing. To connect that field to an editable Vue form system, explore DOM Studio’s named form and field state; keep the actual authentication decision on your server.
Sources
- W3C: Understanding Accessible Authentication (Minimum)
- Google: SMS OTP form best practices
- OWASP: Multifactor Authentication Cheat Sheet
- Vue: Component v-model
- DOM Studio: Form reference
- DOM Studio: Code Input reference
- DOM Studio: Step Up Verification block